
One compromised device. How big could the consequences be?
Recent attacks on supermarket refrigeration systems reveal a growing business risk: when connected equipment is compromised, the damage can extend far beyond the device itself.
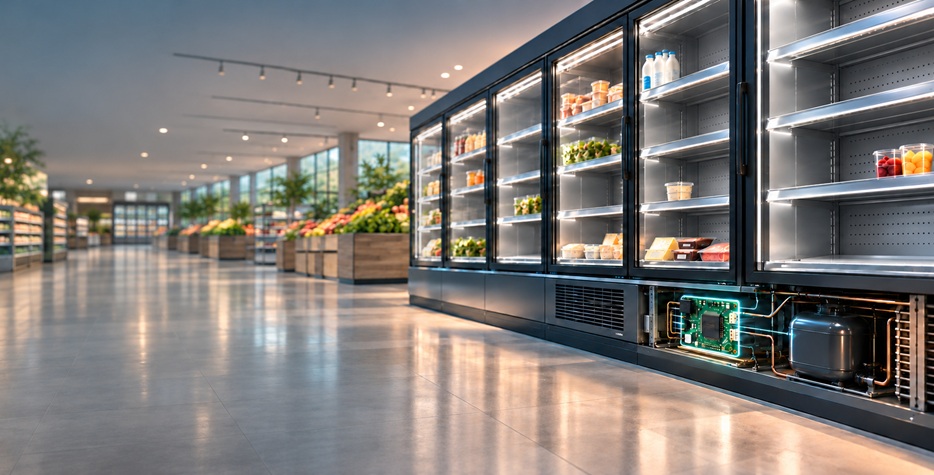
Imagine arriving at your supermarket to discover that your refrigeration systems have been heating up overnight. Food is spoiled. Inventory must be discarded. Operations are disrupted. And the equipment designed to protect your products has become the source of the problem.
In October 2026, attackers remotely manipulated refrigeration systems at around 700 French supermarkets, according to the French government, including approximately 150 Intermarché stores. Temperatures reportedly reached 50°C in some installations and remained there for hours. Stores had to discard their stock, and the owner of Intermarché put the cost at tens of millions of euros. Its insurance did not cover the damage.
On 2 November, similar incidents were reported across Europe. In the Netherlands, at least 17 businesses were affected when attackers altered refrigeration settings remotely.
The attackers didn’t need physical access to the equipment. Weaknesses in connected control systems gave them a way in. Once the damage was done, the question quickly became who was responsible. According to Reuters, a legal fight over liability had already begun.
A small device. A much bigger business risk.
The incidents exposed familiar cybersecurity weaknesses. The French cybersecurity authority linked the attacks to remotely managed refrigeration controllers from several suppliers, including Danfoss, Copeland and Dixell. According to Danfoss, much of the affected equipment was older hardware that was no longer supported. In the Netherlands, a Danfoss spokesperson said the affected systems were accessible outside secured networks and still used default passwords.
The immediate security lessons are clear: protect remote access, remove default credentials and keep systems updated. But the wider implications deserve attention.
Connected controllers, sensors and industrial devices increasingly influence physical operations. They exchange data, receive commands and enable remote services that businesses depend on. A manipulated temperature setting can destroy inventory. An unauthorised command can interrupt production. Untrustworthy device data can influence automated decisions.
For manufacturers, this changes the conversation. Cybersecurity is not simply a technical feature. It is part of the reliability, operational continuity and long-term value customers expect from connected products.
Regulation is moving in the same direction. Under the EU Cyber Resilience Act, manufacturers have had to report actively exploited vulnerabilities in their products since September 2026, and products placed on the EU market from December 2027 must meet its security requirements. Manufacturers are making the design decisions for those products now.
Knowing which device to trust
Basic security hygiene could have prevented many of these attacks. But the attacks also expose a design choice: the affected controllers accepted anyone who knew a shared default password. How can a connected device and the systems around it verify each other’s identities?
A network connection or a software credential does not, by itself, establish that a device is authentic. Hardware-rooted device identity provides an additional foundation for trust.
With SandGrain’s CyberRock, manufacturers can establish a unique identity rooted in hardware for each device and enable authentication without relying on conventional certificates and public key infrastructure (PKI). This allows a service platform to verify the identity of a connected device before accepting it as a trusted participant in an interaction. Unknown devices, or devices unable to prove the required identity, can be rejected. Authentication can also work in the other direction: a device can verify the identity of a communicating party.
CyberRock supports mutual authentication and can enable device-specific, signed commands to be checked locally before execution, without requiring a continuous internet connection. Each device has its own unique identity, avoiding reliance on a shared device credential across an installed base. A compromise of one device does not, by itself, expose the identities of all other devices.
The same foundation can support authentication throughout the device lifecycle, from manufacturing and deployment to maintenance and end of life.
Importantly, authenticating a device is not the same as authorising a person or a command. Secure remote maintenance also requires appropriate controls to authenticate service tools and users, authorise permitted actions and protect communications. Signed-command verification is one component of that wider security architecture.
Device identity is not the complete security solution. It is a foundation for establishing trusted device interactions.
The time to build trust is before something goes wrong
Refrigeration is only one example.
The same questions apply to industrial sensors feeding automated production systems, connected devices in energy installations and edge equipment processing valuable operational data.
Can the system verify which device produced the data? Can it distinguish an authentic device from an unknown or cloned one? Can manufacturers maintain that trust as products remain in operation for years?
Connected equipment has never been easier to build and deploy, and never easier to copy, impersonate or manipulate. Yet many connected systems still rely on credentials and processes that can be difficult to manage securely across large fleets and long operational lifetimes.
Digital capability is scaling faster than digital trust.
SandGrain helps close that gap by making device identity verifiable and anchoring it in silicon.
Are you designing your next generation of connected equipment, or responsible for a large installed base?
Let’s talk about how hardware-rooted device identity can help strengthen trust in your products and support their security throughout the lifecycle.
Sources:
- Reuters, 12 October 2026 — French supermarket refrigeration attacks
- Reuters, 2 November 2026 — Further attacks across Europe
- NOS, 2 November 2026 — Attacks affecting 17 Dutch businesses
- AP, 13 October 2026 — French government: around 700 supermarkets affected
- CERT-FR, 12 October 2026 — Alert on compromised refrigeration controllers
- Reuters / AFP, October 2026 — Costs, insurance and liability (Les Mousquetaires, Intermarché)
Share this article


Explore more insights
What happens if someone copies an AI model from a device in the field?
Consider a reconnaissance vehicle equipped with an AI vision model trained to recognise objects in difficult terrain. That model represents valuable intellectual property, developed through years of collecting and labelling data, training algorithms and refining performance.
SandGrain appoints Jan Jager as CEO to bring trusted device identity to a connected world
New CEO to accelerate CyberRock adoption through customer collaboration, strategic partnerships and international growth
Being connected doesn’t make a device trustworthy
Recent cybersecurity incidents in the retail sector raise a broader question: how much trust do organisations place in connected systems without knowing whether the devices within them are genuinely trustworthy?